
AgentAvow Trust MCP Server
@AgentAvow
基本情報

AgentAvow Trust MCP Server について
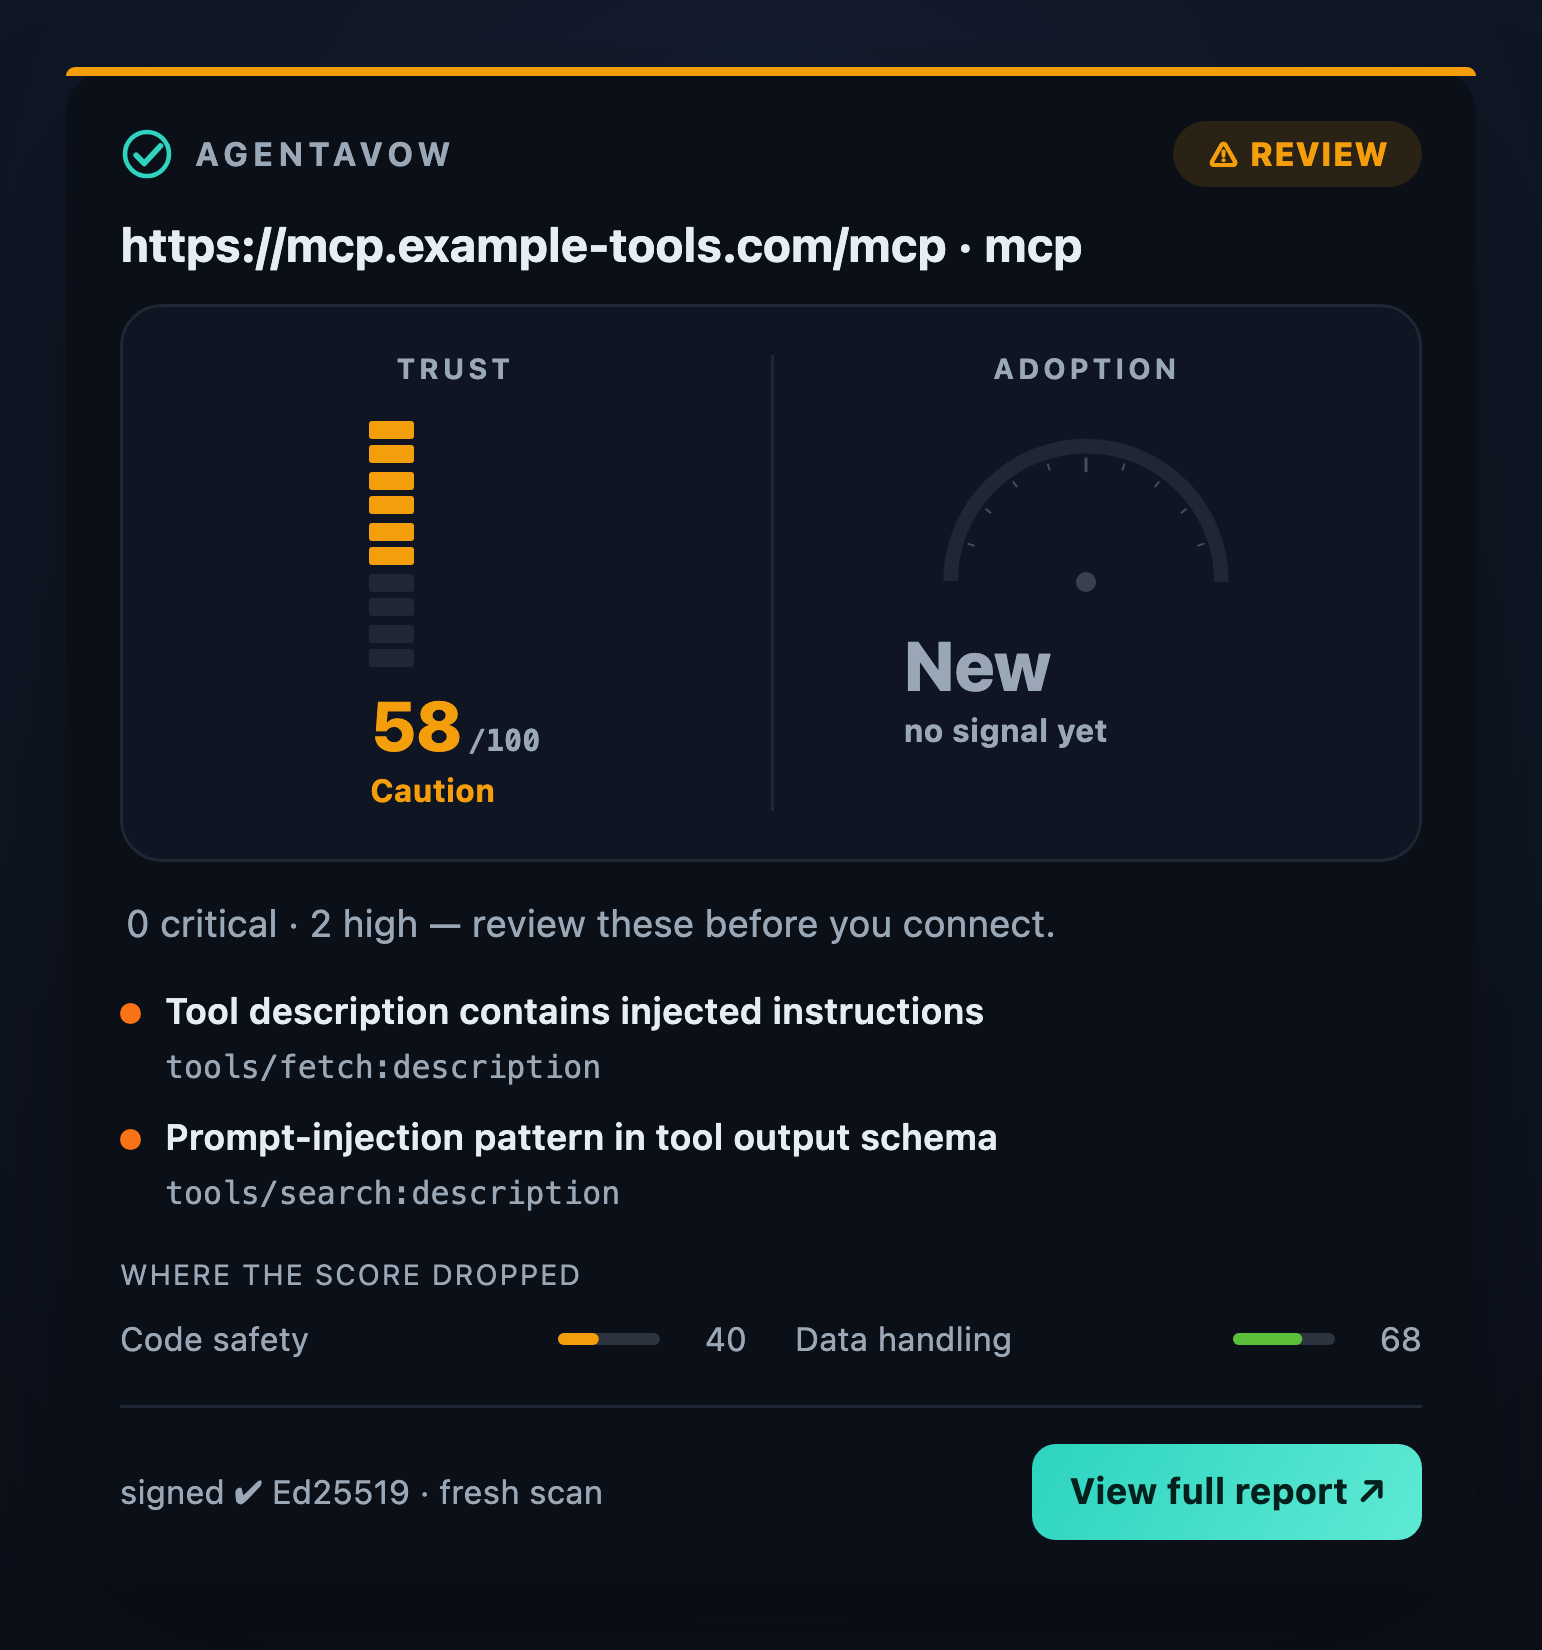
Trust verification and security scanning for AI agents. Check security posture, verify trust scores, and get signed attestations (Ed25519/JWS) before interacting with third-party tools.
AgentAvow Trust MCP Server の設定
以下の設定を使って、このサーバーを MCP 対応クライアントに追加してください。
{
  "mcpServers": {
    "agentavow": {
      "type": "http",
      "url": "https://agentavow.com/mcp"
    }
  }
}
AgentAvow Trust MCP Server のツール
ツール一覧はまだありません
この掲載には表示できるツール一覧がまだありません。サーバーにツールがないという意味ではありません。対応機能はプロジェクトのドキュメントをご確認ください。
上のボタンでサーバーのエンドポイントに接続し、ツール一覧を取得できます。
概要
What is AgentAvow Trust?
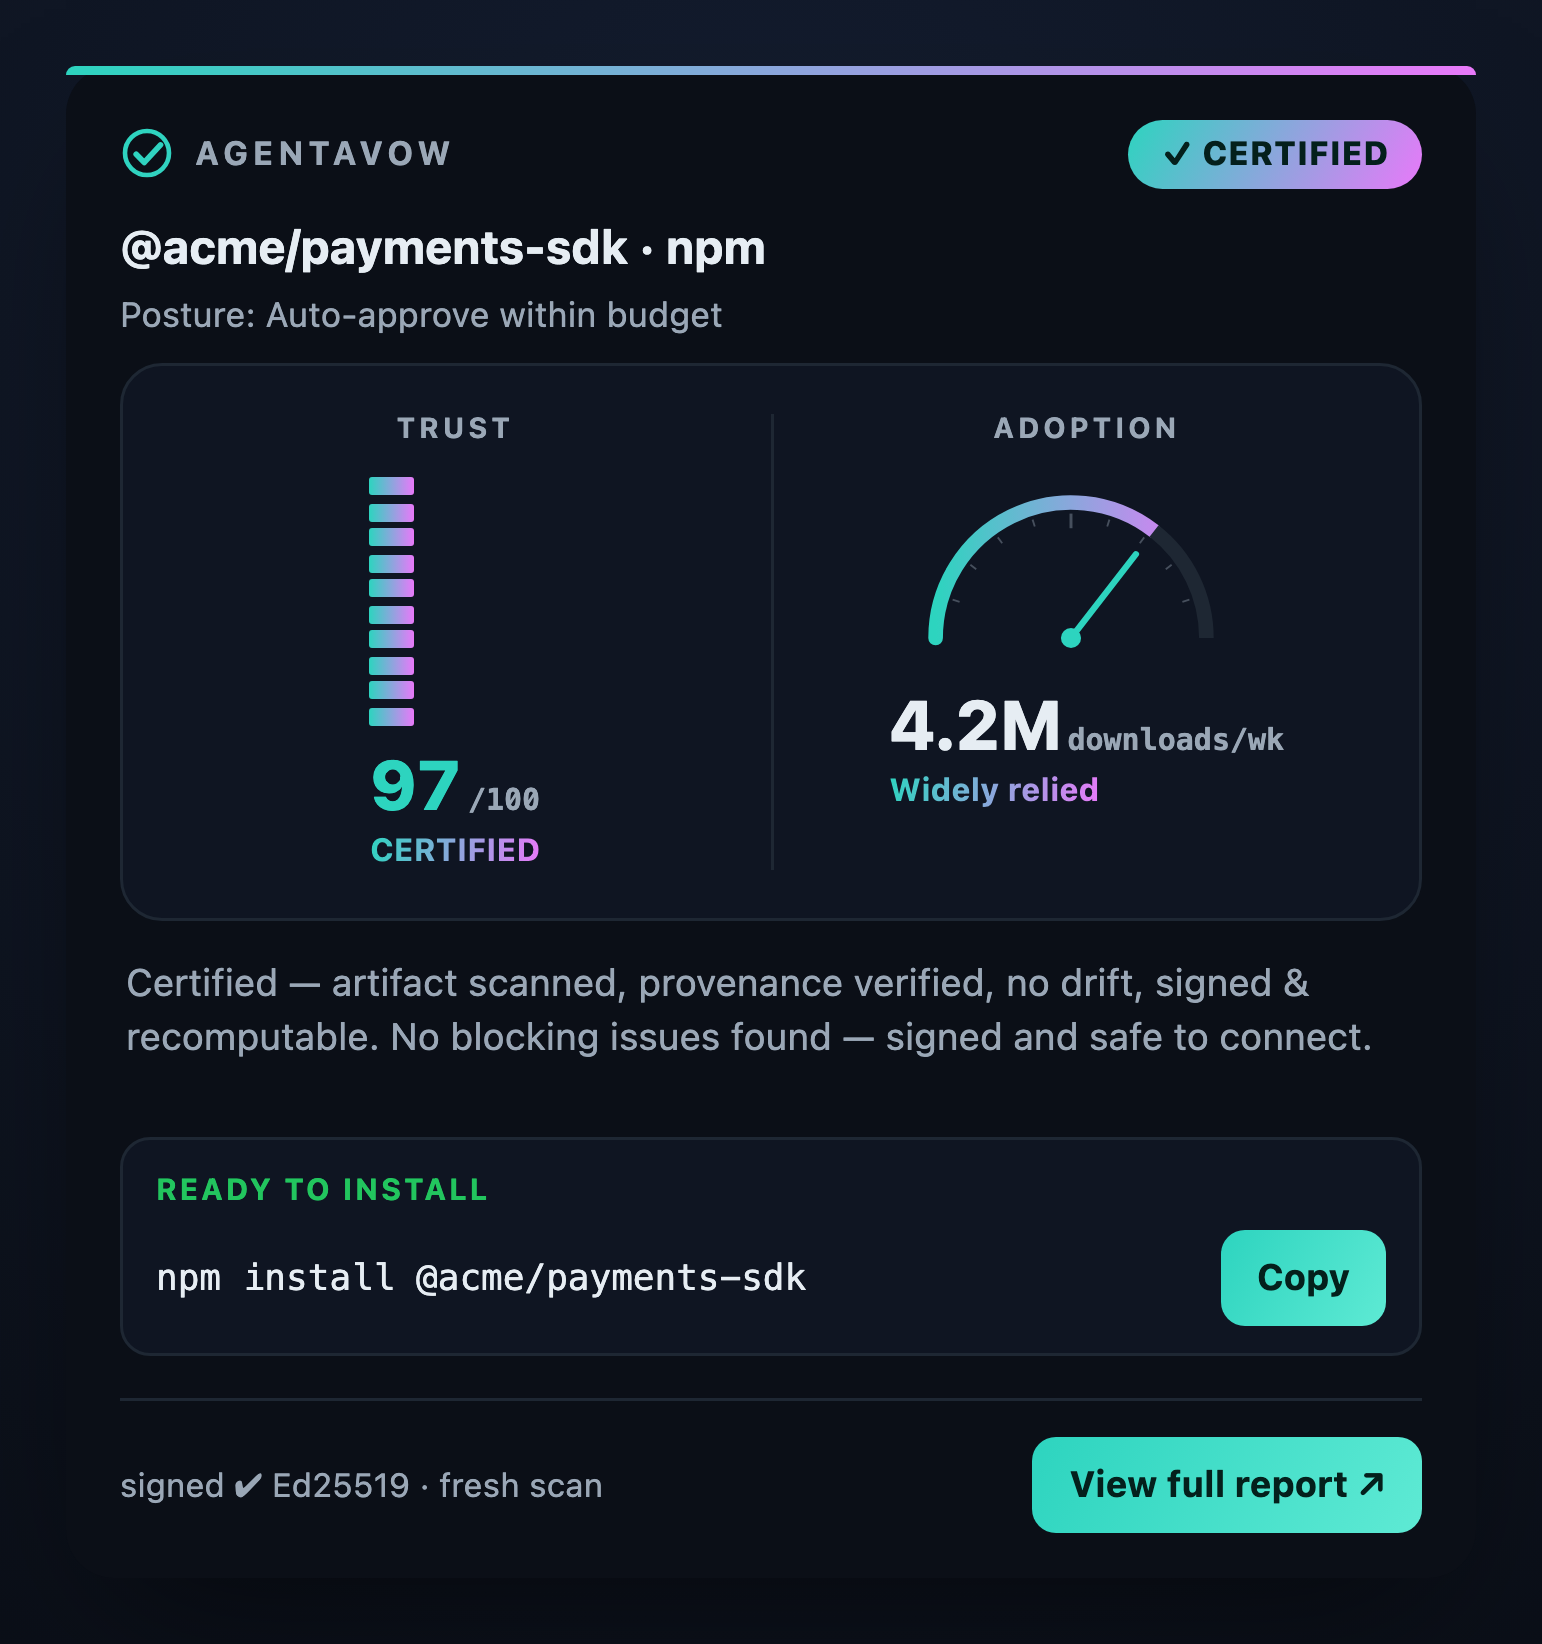
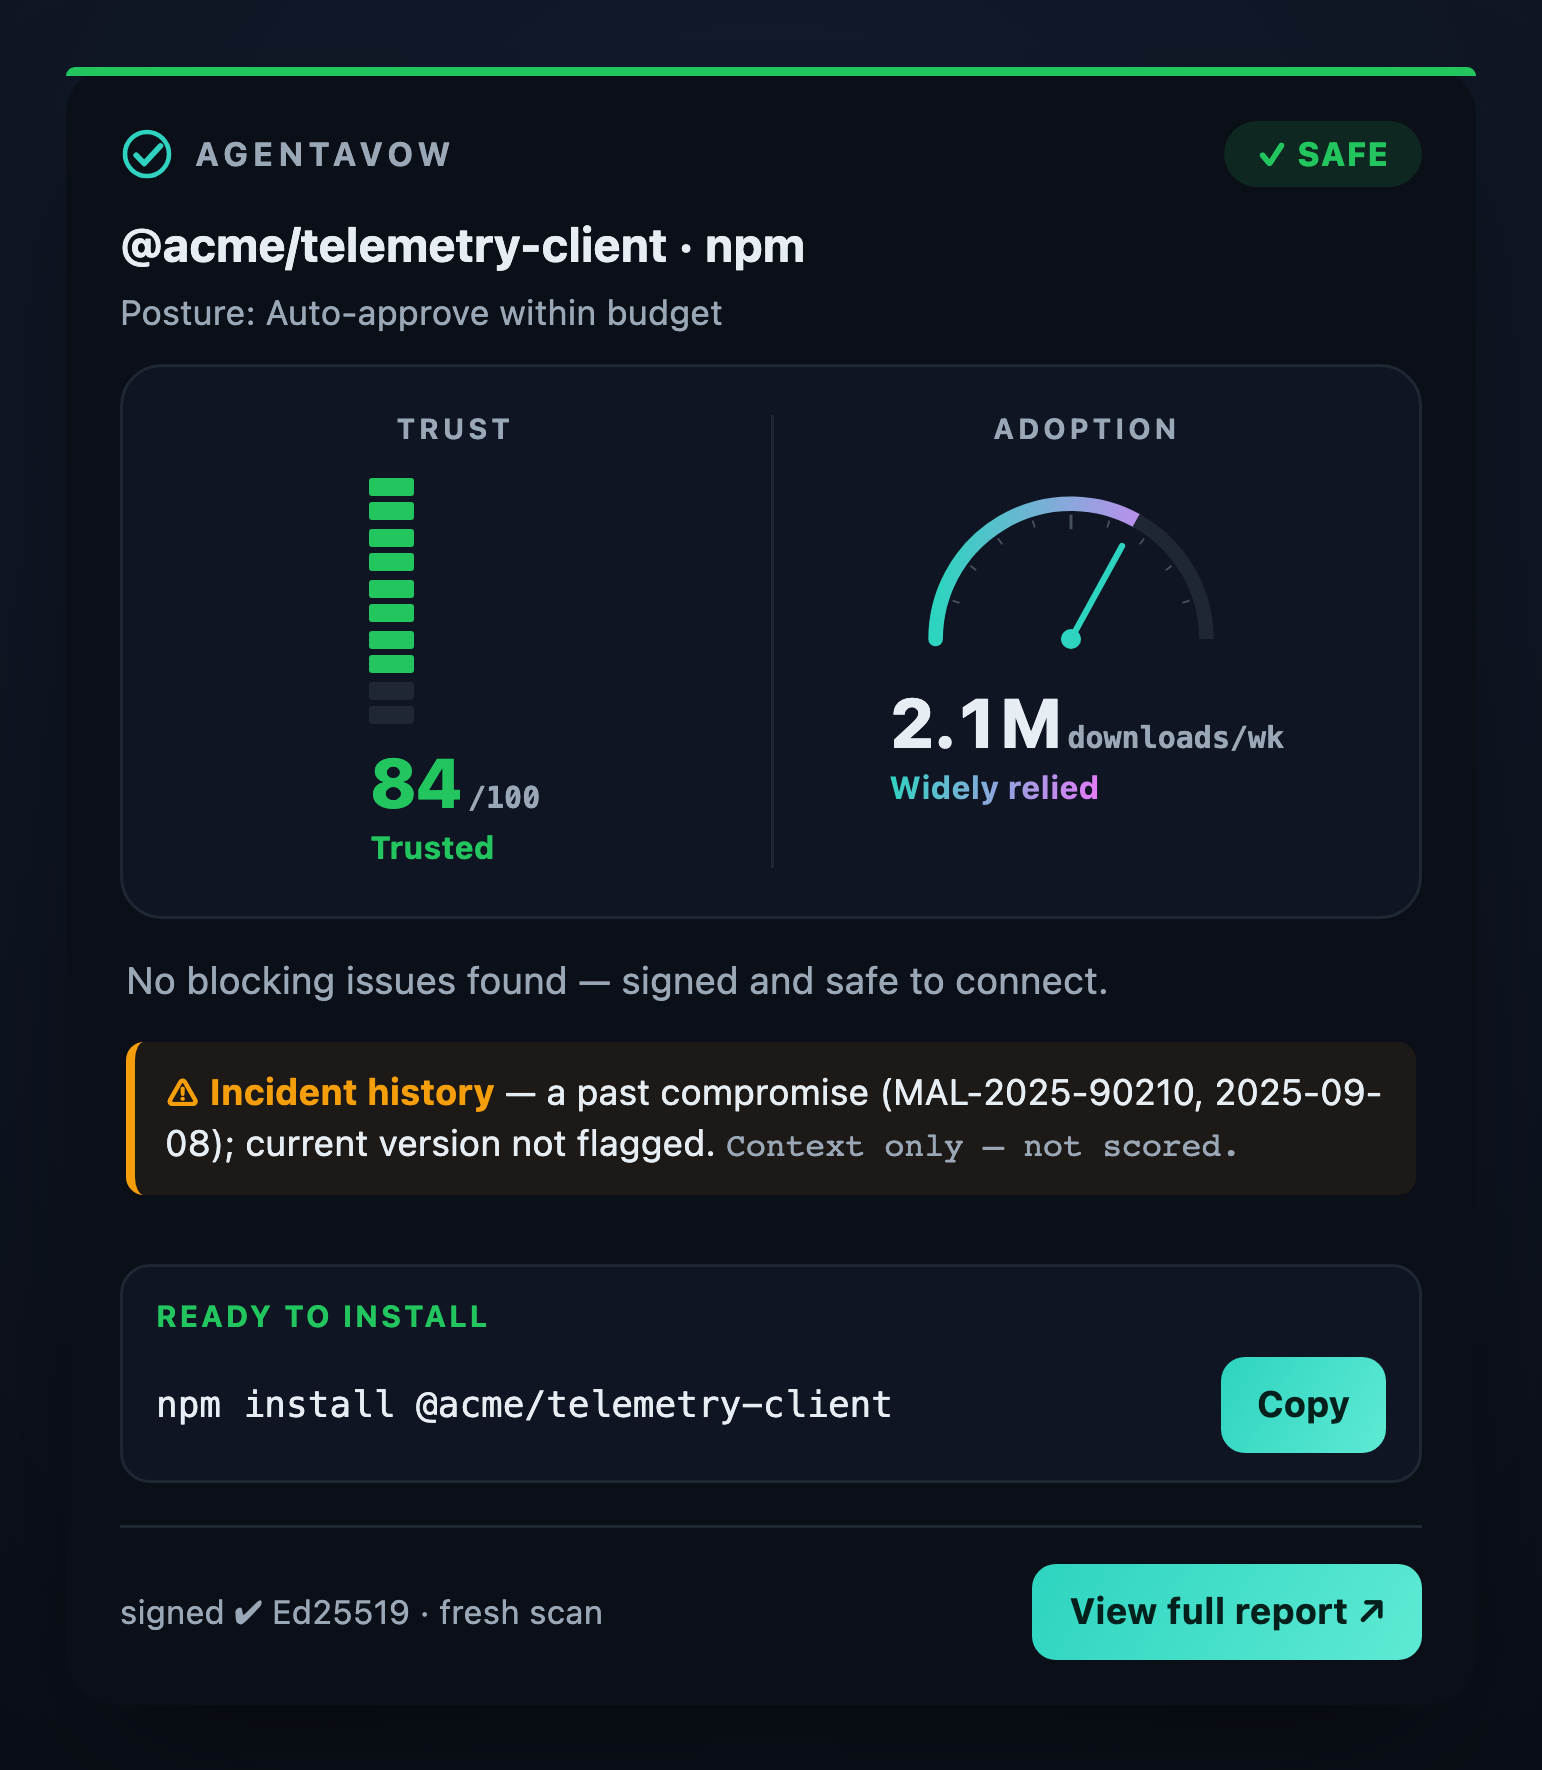
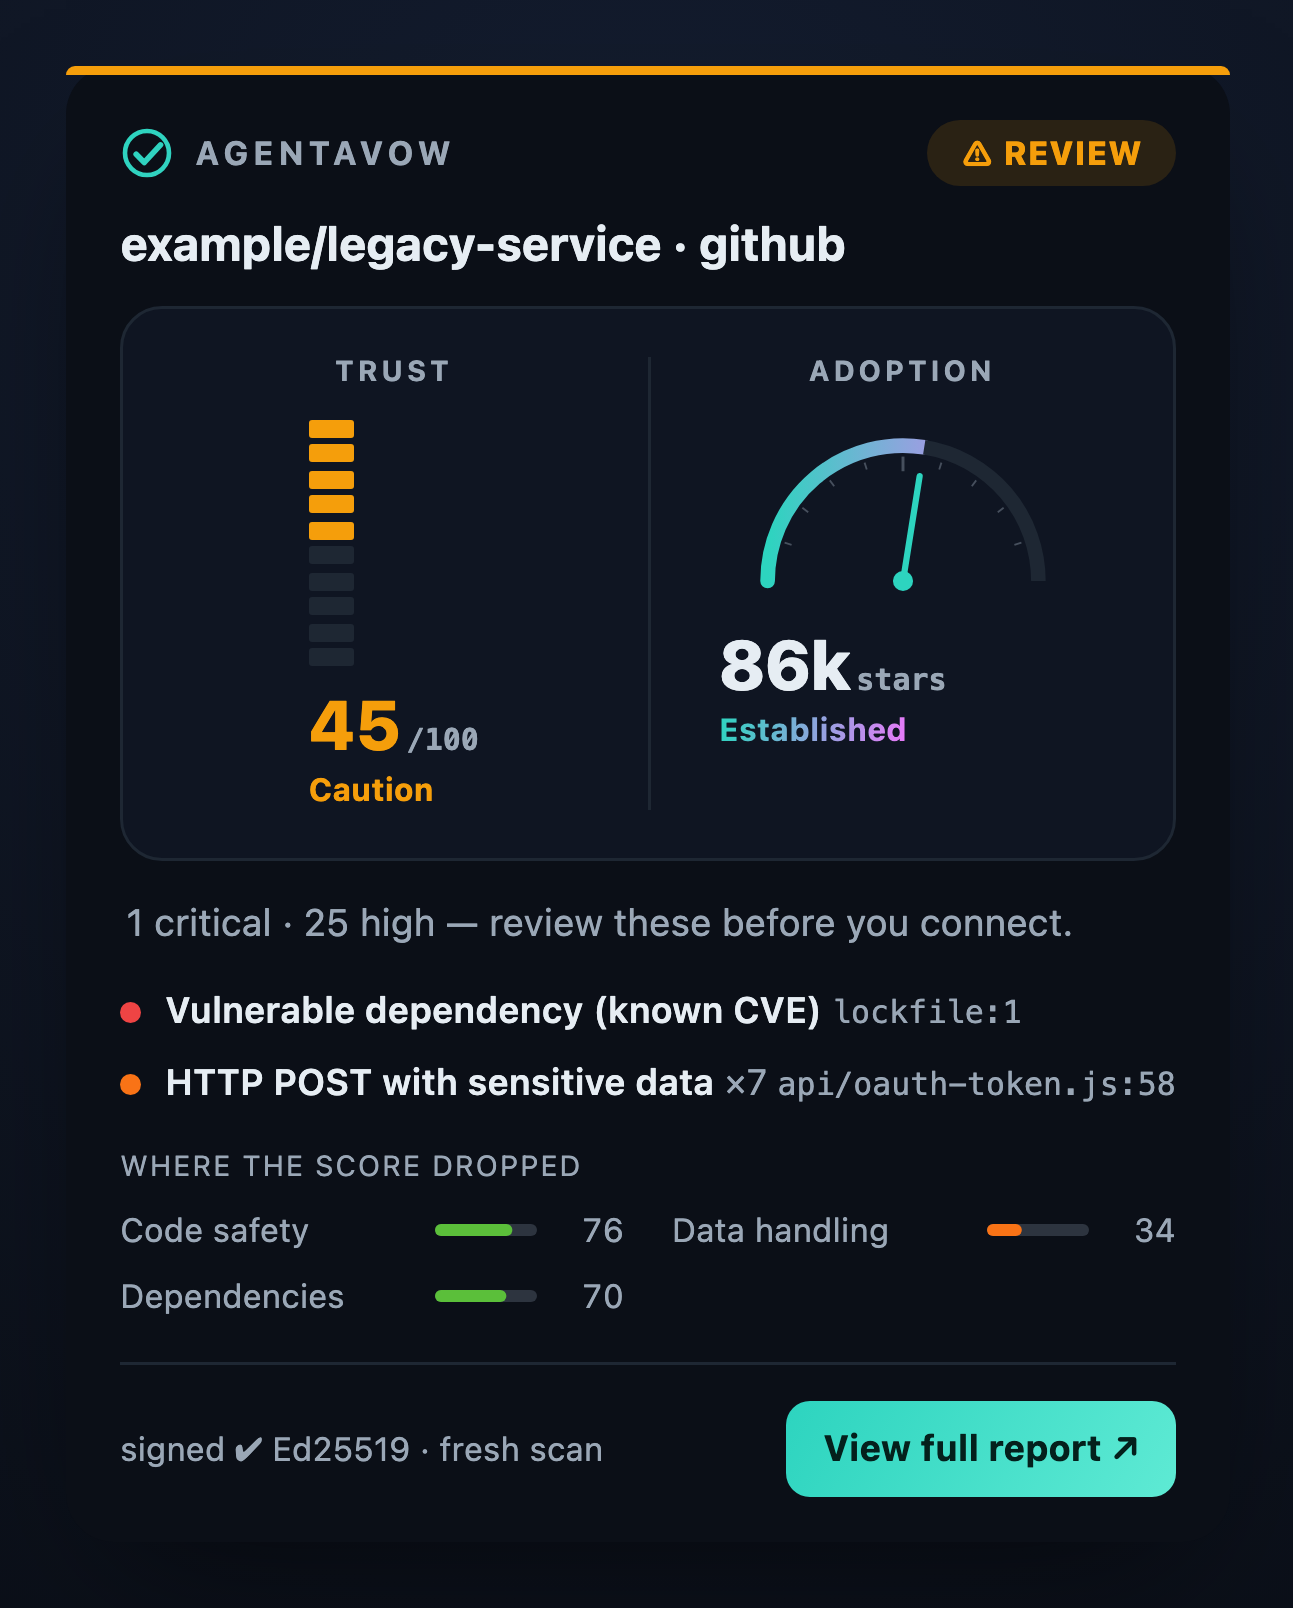
AgentAvow Trust is an MCP server that grades the safety of anything an AI agent connects to — a GitHub repo, an MCP server, or an npm/PyPI/crates/Docker/Hugging Face package. It returns a signed, 0–100 trust score with a plain safe / needs-review verdict, backed by scan evidence anyone can recompute offline. Read-only and authless: no account, no keys.
How to use AgentAvow Trust
Add the remote server to your MCP client (Claude Code, Cursor, or your own runtime) — no install:
claude mcp add --transport http agentavow https://agentavow.com/mcp
Then ask it to check a tool before you connect: "scan the repo modelcontextprotocol/servers" or "scan the npm package chalk." Every result links to a full report and a signed attestation you can verify offline.
Key features
- Signed, offline-recomputable verdicts — Ed25519/JWS over an RFC 8785 canonical verdict; recompute it byte-for-byte against the public JWKS, no callback required.
- 12-category static analysis — secret hygiene, unsafe code execution, data handling, dependencies, prompt-injection surfaces, and more; every finding points at the exact file and line.
- Scans across surfaces — GitHub repos, live MCP servers (it checks the tool definitions for poisoning/injection), and npm/PyPI/crates/Docker/Hugging Face packages.
- Eight read-only tools — scan_repo, scan_package, scan_mcp_server, verify_trust, check_interaction_safety, lookup_identity, get_trust_badge, about_agentavow.
- Authless — anonymous and read-only; nothing to configure.
Use cases
- Scan an MCP server or package before your agent connects, so an unsafe tool is stopped in the loop rather than found after the fact.
- Gate CI on a minimum score with the GitHub Action or CLI.
- Check the interaction-safety threshold before delegating to or trading with another agent.
- Add a signed trust badge to your README that anyone can verify.
FAQ
- Do I need an account? No — anonymous and read-only.
- Is it free? Yes, checking is free.
- Can I verify a score without trusting AgentAvow? Yes — recompute the canonical verdict and check the Ed25519 signature offline against the public JWKS.
「AI とエージェント」の他のコンテンツ
Legion MCP
faulkjMCP-native LLM councils for debates, juries, blind panels, voting, refinement, and custom multi-model deliberation.
bsv.cx
Andy RoweTimestamp and verify evidence on-chain. Let your agent prove what it saw and when. bsv.cx gives an AI agent verifiable memory. Timestamp a hash of any output, archive a web page as it looked, or fetch a URL with a recei
fhirHydrant
faulkjOpen-source Node.js FHIR MCP server with SMART Backend Services, metadata-aware search/CRUD tools, compact responses, FHIRPath filtering, safe pagination, audit events, and terminology lookup.

OpenZiti / LLM-Gateway
openzitiNetFoundry LLM Gateway is an OpenAI-compatible API proxy that routes requests across multiple LLM providers using zero-trust networking. Zero trust LLM gateway. OpenAI-compatible proxy with semantic routing and load bala
Krafters
Krafters (Romain Duclos)Krafters is a French club of specialized AIs for freelancers and small businesses. Its connector opens the member's AI kits for Facebook and Instagram ads, SEO/GEO and short videos directly in Claude, and gives the next
コメント