
Deltabridge製品認証済み注目
AI-native cyber threat intelligence. Ask Athena for cited analysis on threat actors, malware and CVEs, and turn noisy feeds into decision-ready briefs.
Deltabridge について
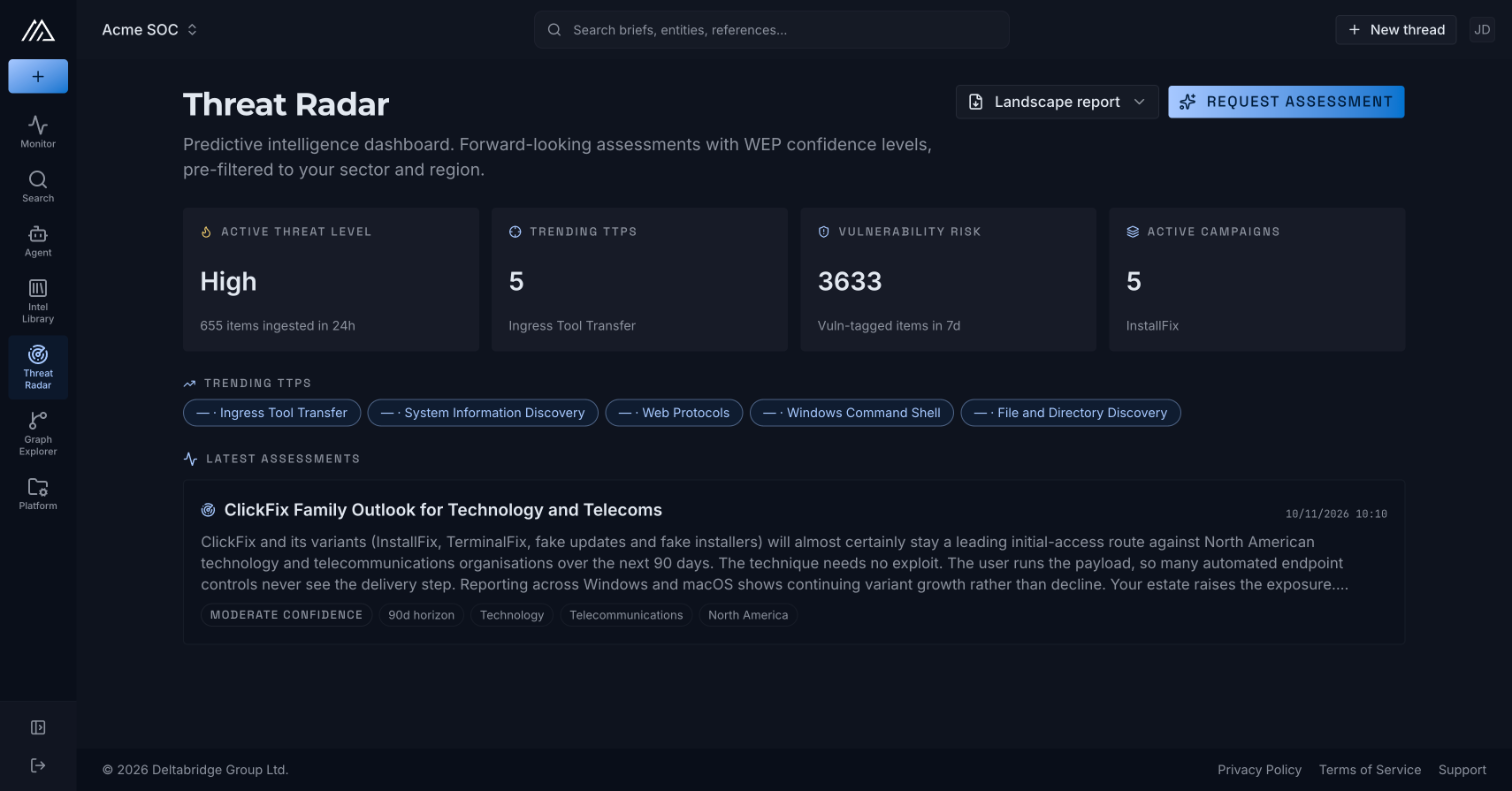
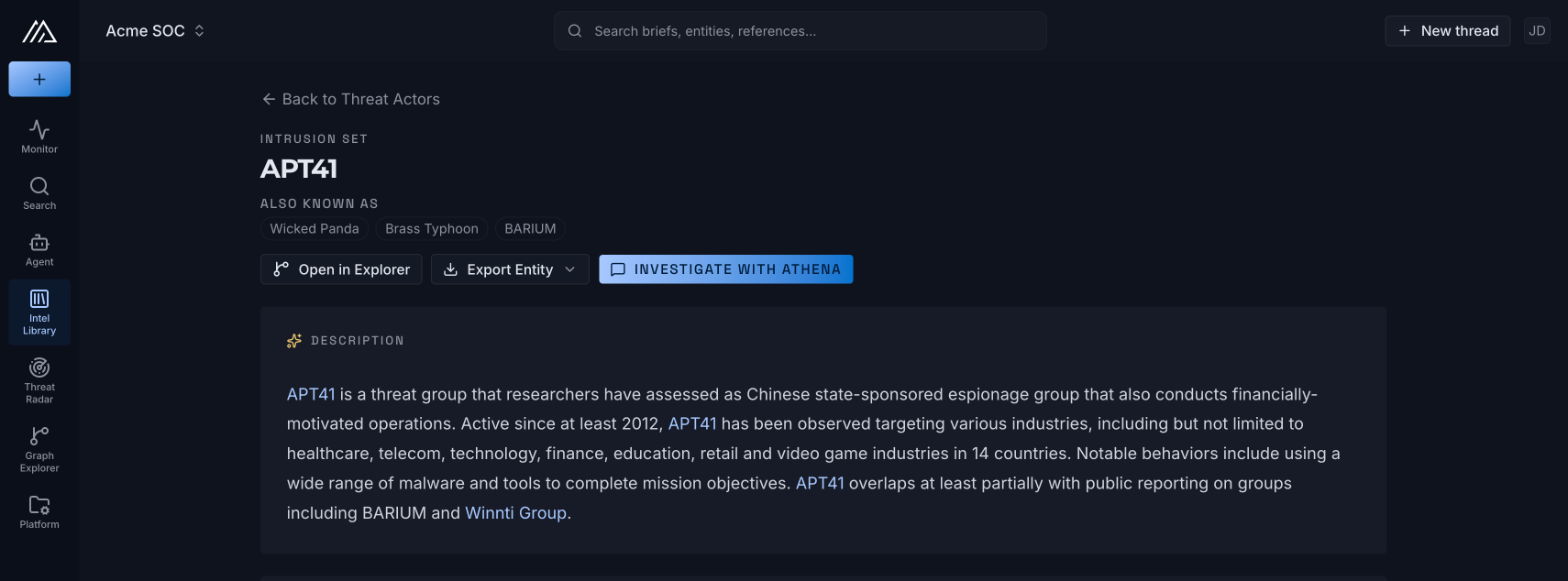
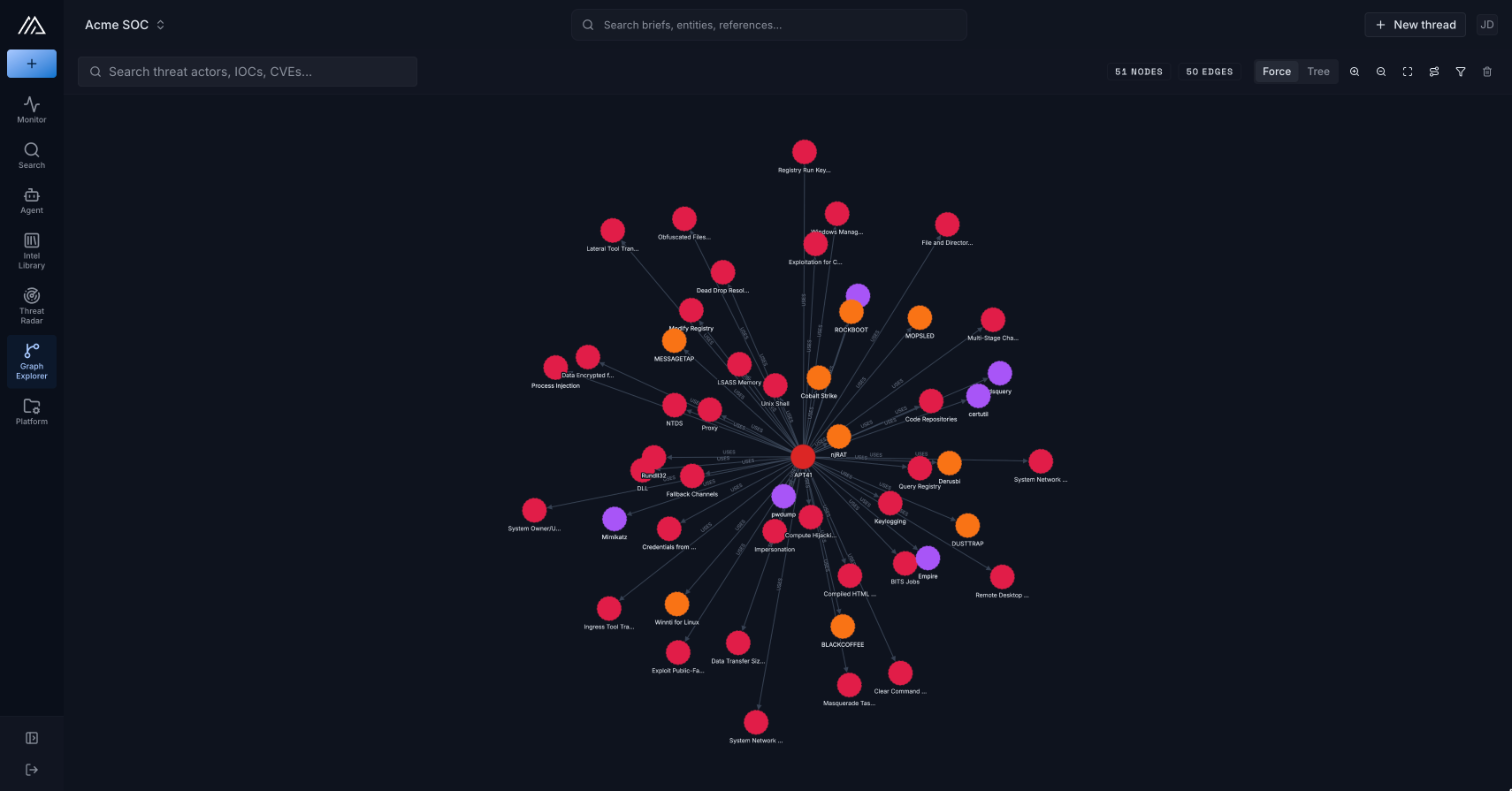
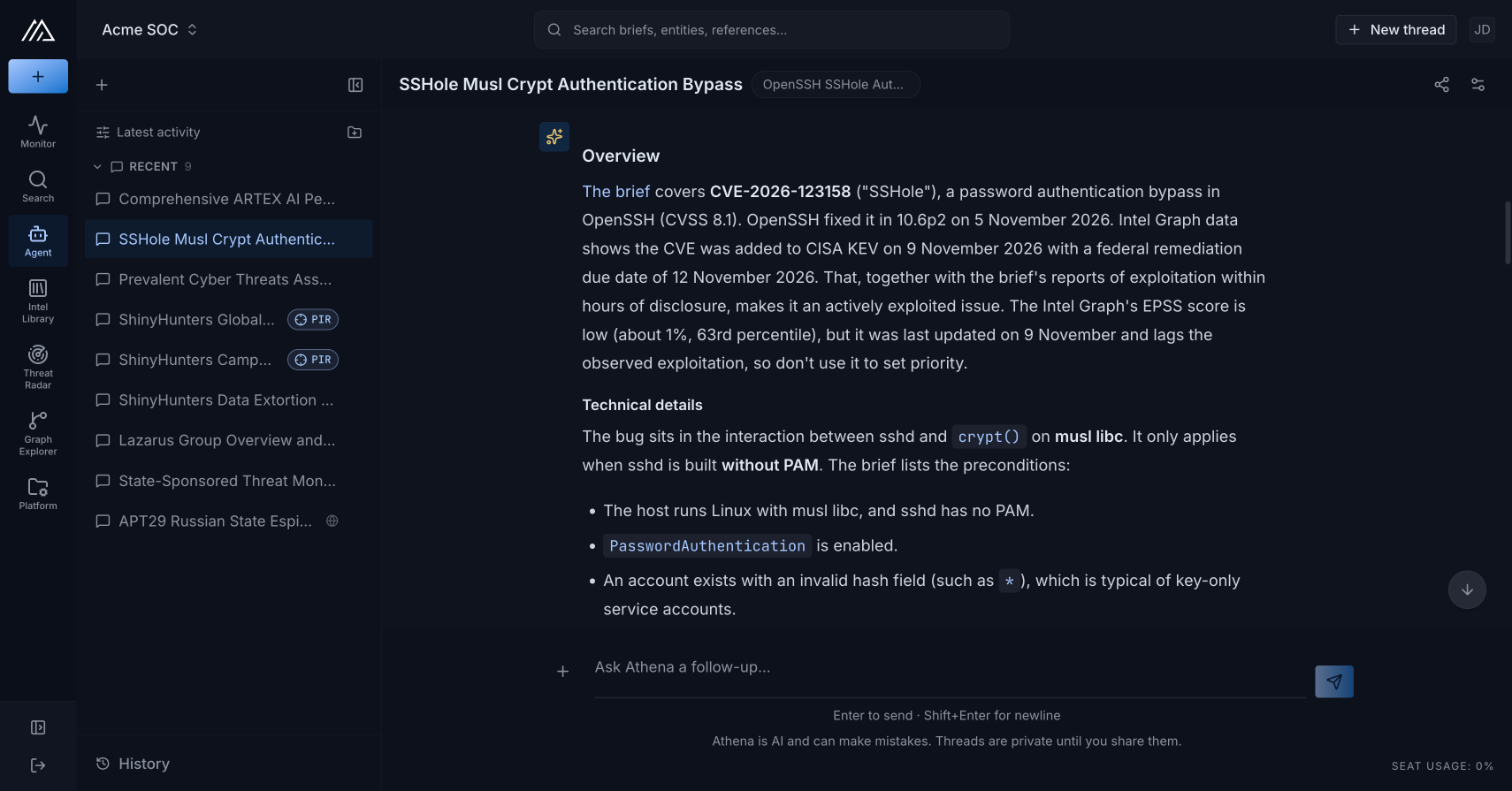
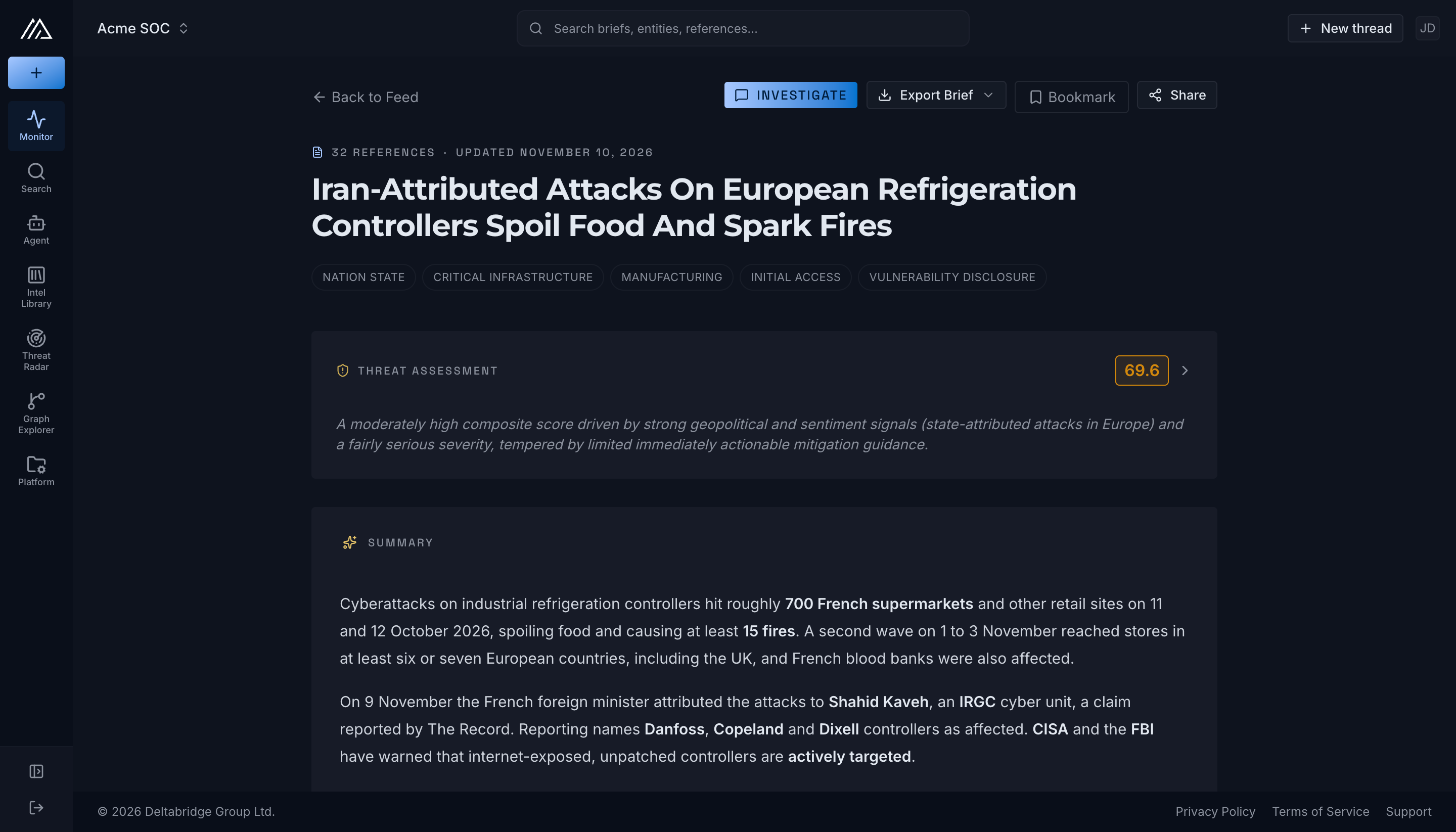
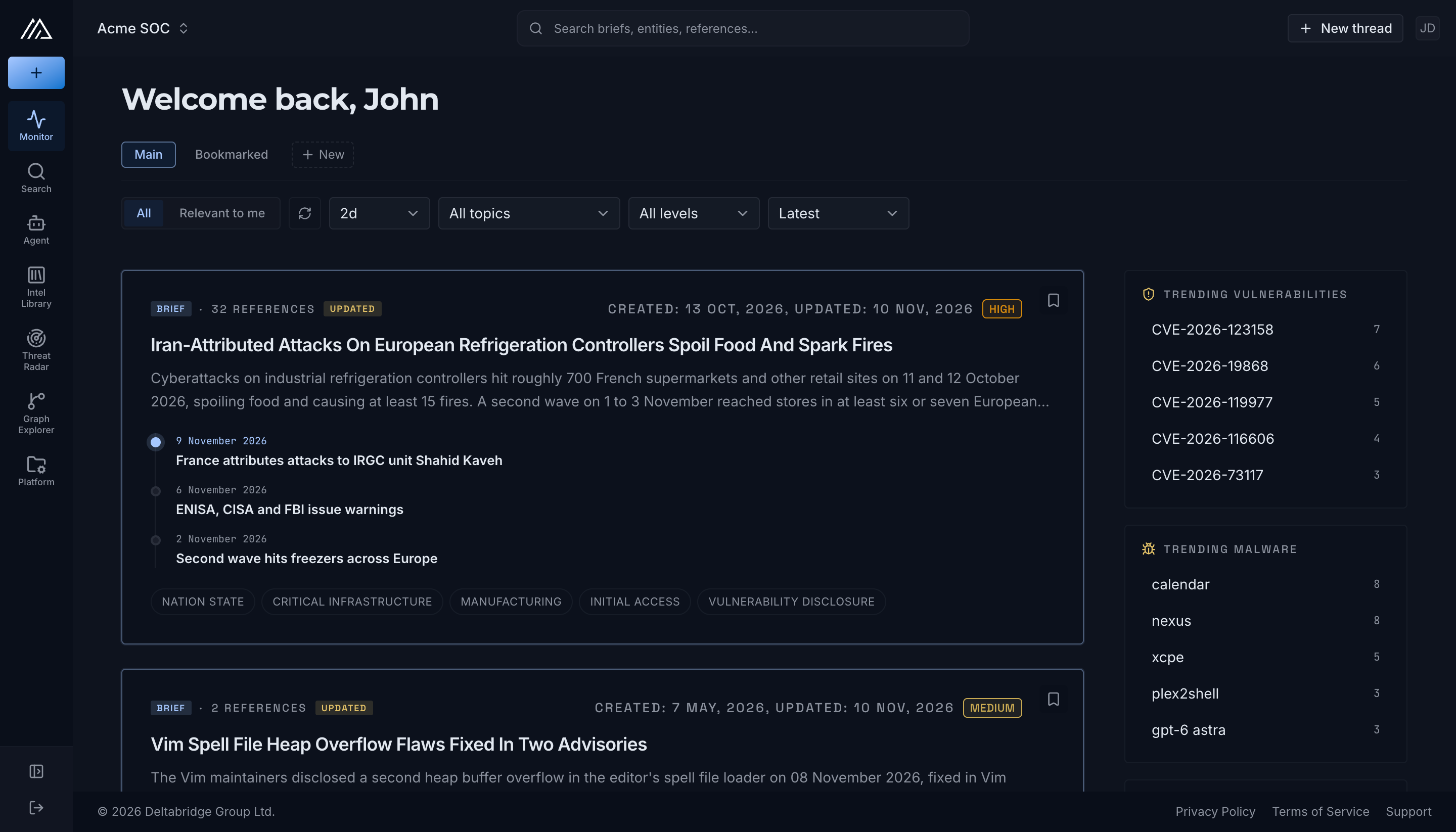
Deltabridge is a cyber threat intelligence platform that does the reading for security teams. It monitors 300+ public sources, including threat feeds, vendor advisories, vulnerability databases and security research, and turns them into intelligence you can act on. What it does: - Intelligence briefs. Athena, Deltabridge's AI analyst, synthesises related reporting into concise briefs. Each brief has a summary, narrative, timeline, threat score, affected sectors and countries, linked entities and indicators, and shows how many sources it draws on. Briefs update as new reporting arrives. - Athena, the AI analyst. Ask questions in plain language. Athena searches your intelligence, follows relationships across the threat graph and answers with the briefs and entities it used. - Intel Library and threat graph. Threat actors, malware, tools, campaigns, vulnerabilities and MITRE ATT&CK techniques, all connected. You can see who uses what, which CVEs are being exploited, and how actors map to techniques. - IOC lookup and enrichment. Check IPs, domains, URLs and hashes against known intelligence and enrich them with external sources. - Threat Radar and Deep Research. Assessments tailored to your organisation's profile, plus in-depth research reports on a topic, actor or vulnerability. - Scheduled investigations. Recurring questions Athena runs for you, with results delivered on a schedule. - CISA KEV and ATT&CK built in, alongside CVE data and detection context for techniques. MCP integration for AI agents: Deltabridge includes a remote MCP server at https://api.deltabridge.ai/mcp. You can connect Claude, ChatGPT, Cursor, VS Code or any MCP client, and your agent can then: - search briefs, actors, malware, CVEs, techniques and IOCs; - explore the threat graph; - read your threads and assessments; - use built-in analyst workflows: entity profiles, IOC investigations, CVE exposure and sector briefs. Access uses OAuth 2.1 with per-client consent, and admins can revoke clients at any time. Only two tools write to your workspace, enrichment and saving a public URL; everything else is read-only. Who it's for: SOC analysts, threat intelligence teams, security engineers, MSSPs and security leaders who need current, relevant threat intelligence without reading every feed themselves. Pricing: paid plans from $29 a month, and a 14-day Business trial. MCP access is included on Researcher, Business and Enterprise.
コメント
その他のエージェント

AI Hairstyle Changer
aihairstylechanger.ai
Upload your photo and preview 100+ trendy hairstyles with AI hairstyle changer — results in seconds.

Adspy.sh
adspy.sh
Adspy brings Meta and Google ads into your AI assistant. Ask about any brand's ads, read how each one is built, and save the ideas worth sharing.
BlogSEO
BlogSEO
Put your SEO on autopilot. BlogSEO analyzes your site, writes daily articles matching your brand voice, and publishes automatically.
ChatGPT充值
getgptplus.app
GetGPTPlus 提供 ChatGPT Plus、Pro 与 Codex 国内充值升级服务,支持支付宝、微信支付,无需海外信用卡或提供账号密码。用户可购买卡密后在自己的 ChatGPT 账户中完成兑换,页面包含套餐价格、充值流程、视频教程、常见问题、订单查询与售后说明,帮助国内用户快速完成开通、续费和异常处理。
Cowboy MCP
cowboymcp.com
Manage a self-hosted WordPress site with ChatGPT, Claude, or any AI — posts, WooCommerce, plugins & security, in plain English. Free, open-source MCP server.
DolphinRadar
dolphinradar.com
Boost your Instagram strategy with DolphinRadar. Analyze follows, likes & audience trends with AI—fast, private, and 100% platform compliant.