
AgentAvow Trust MCP Server
@AgentAvow
基本信息

关于 AgentAvow Trust MCP Server
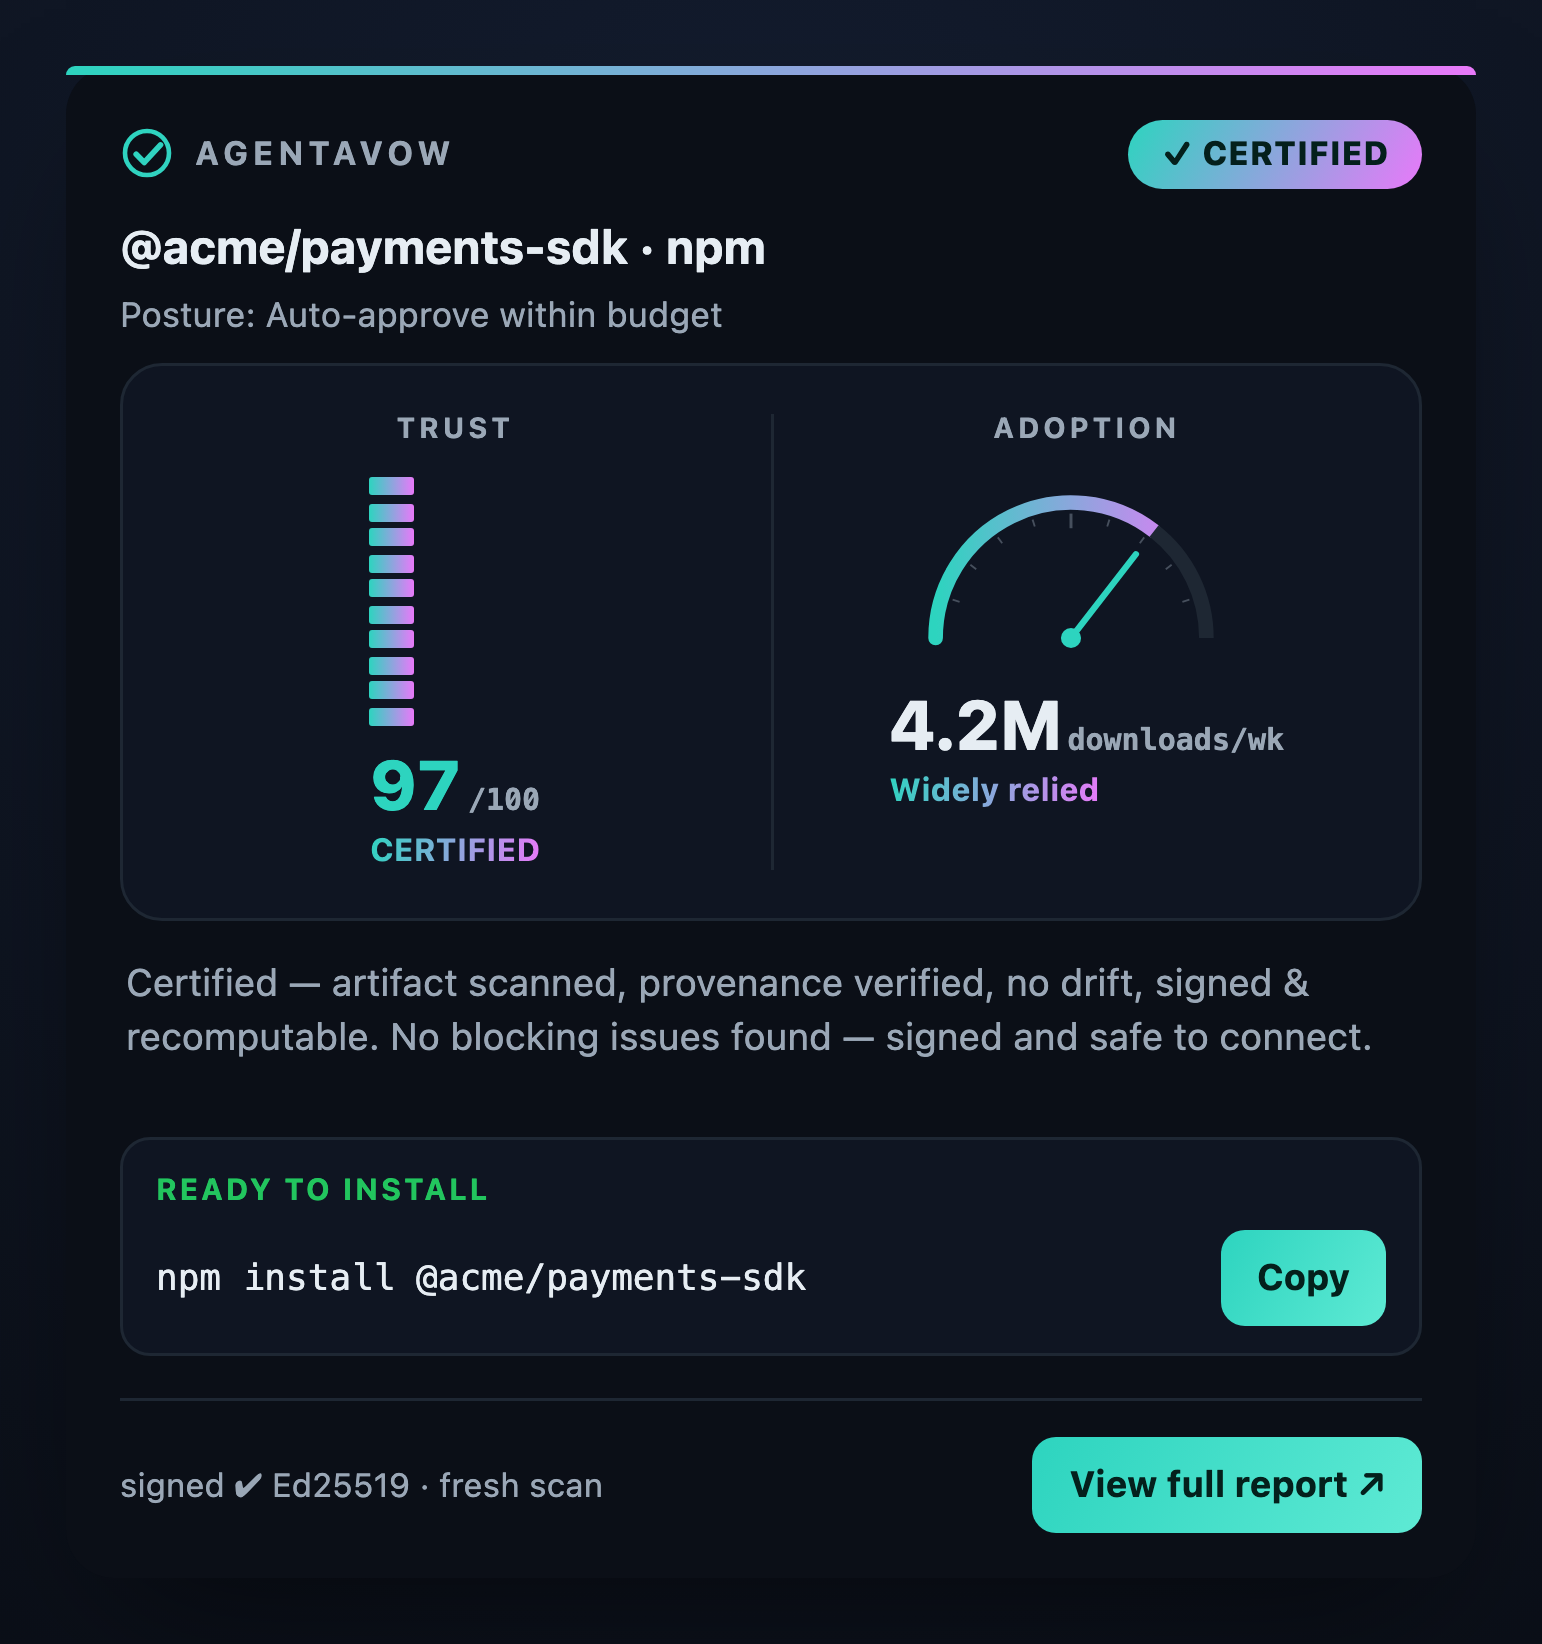
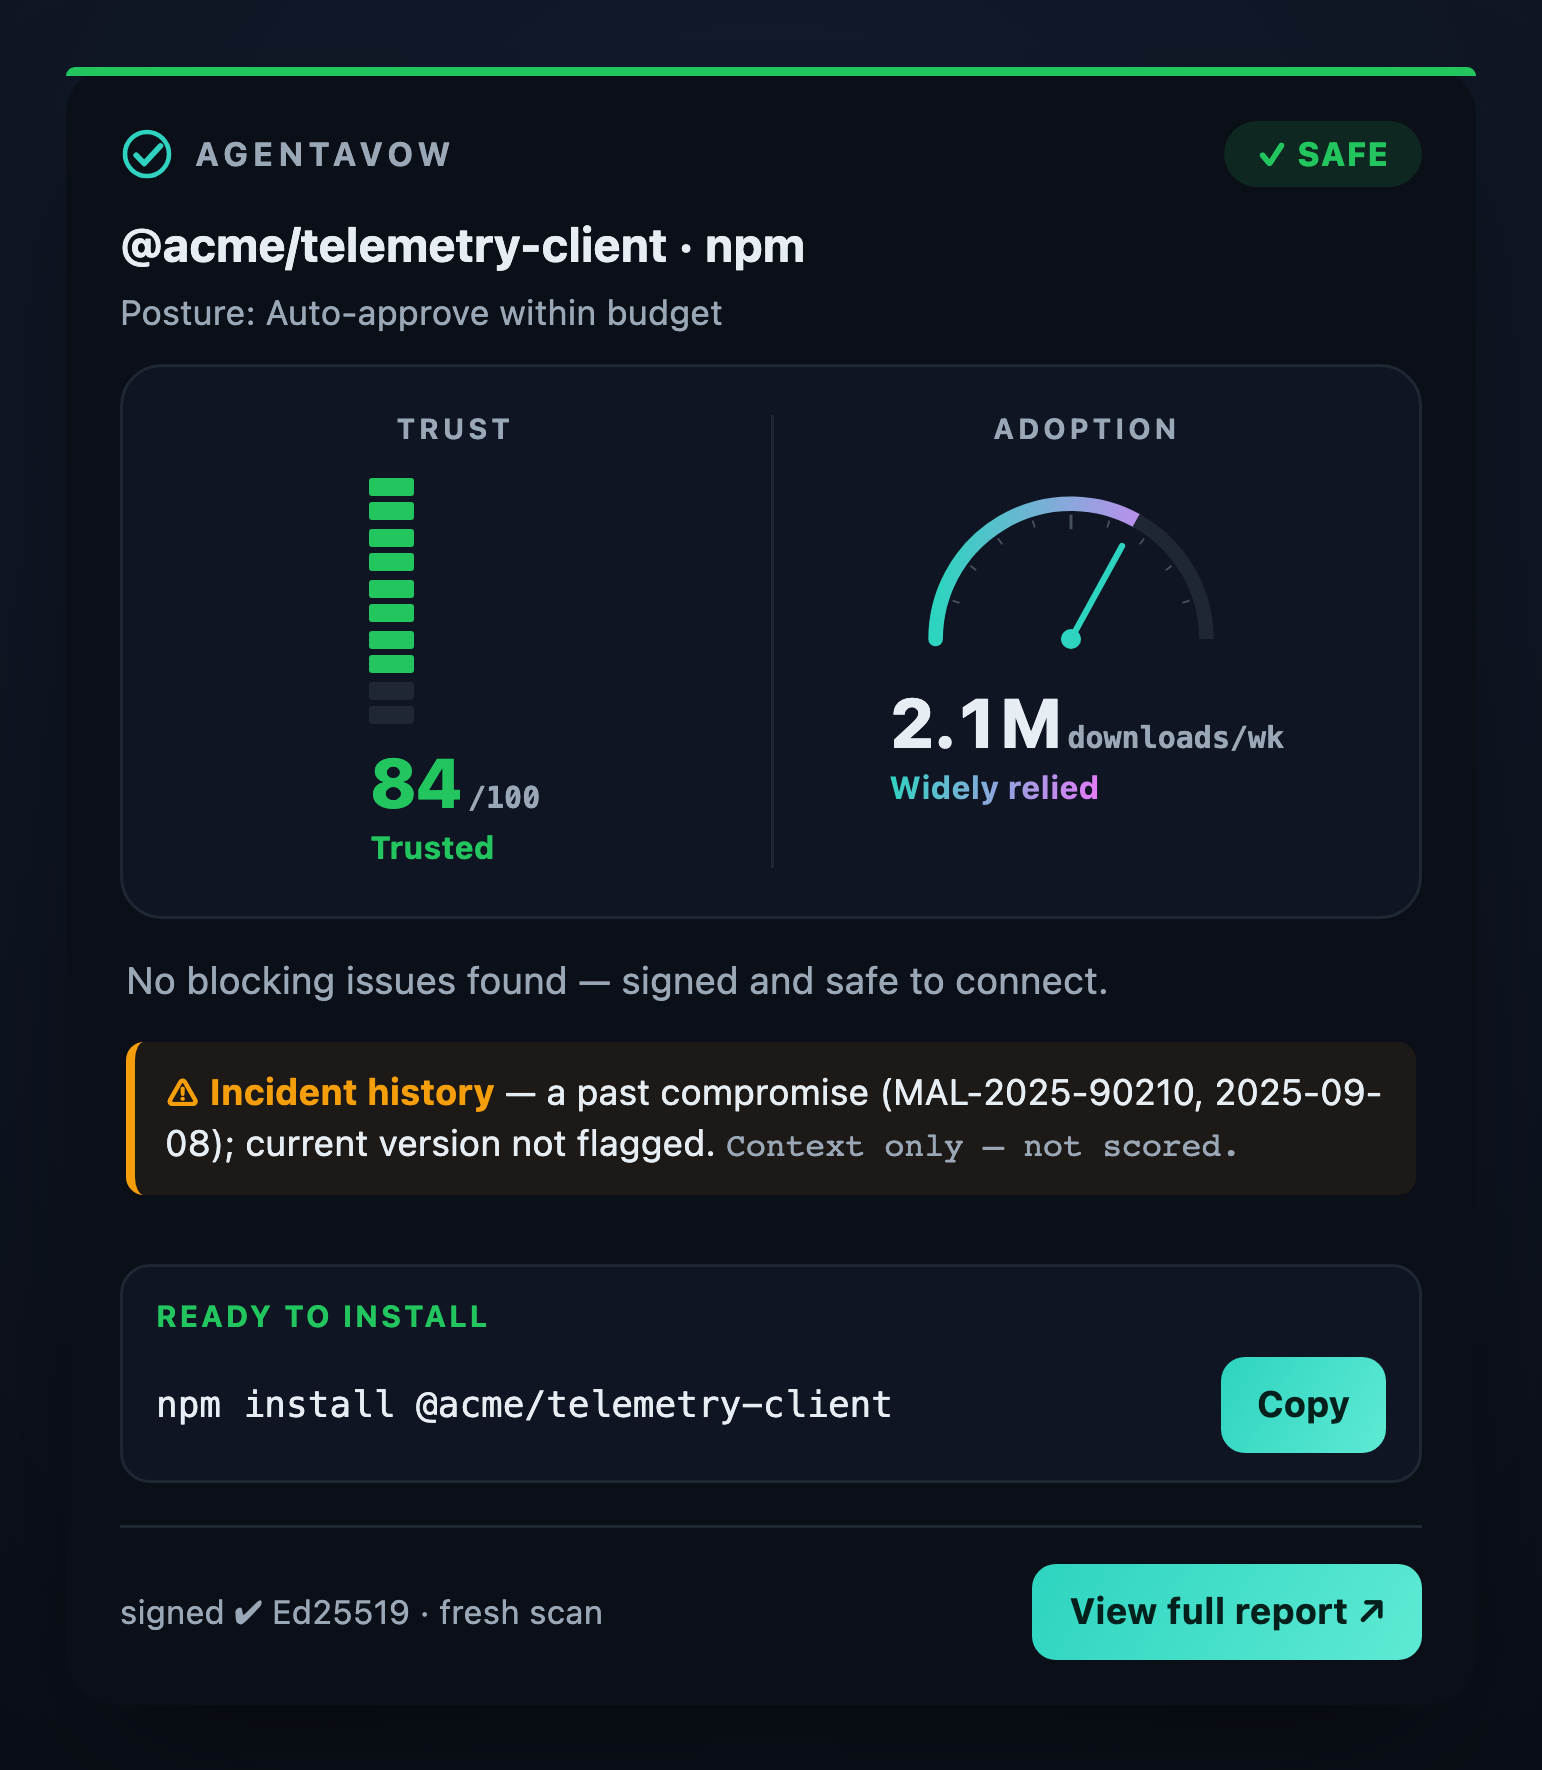
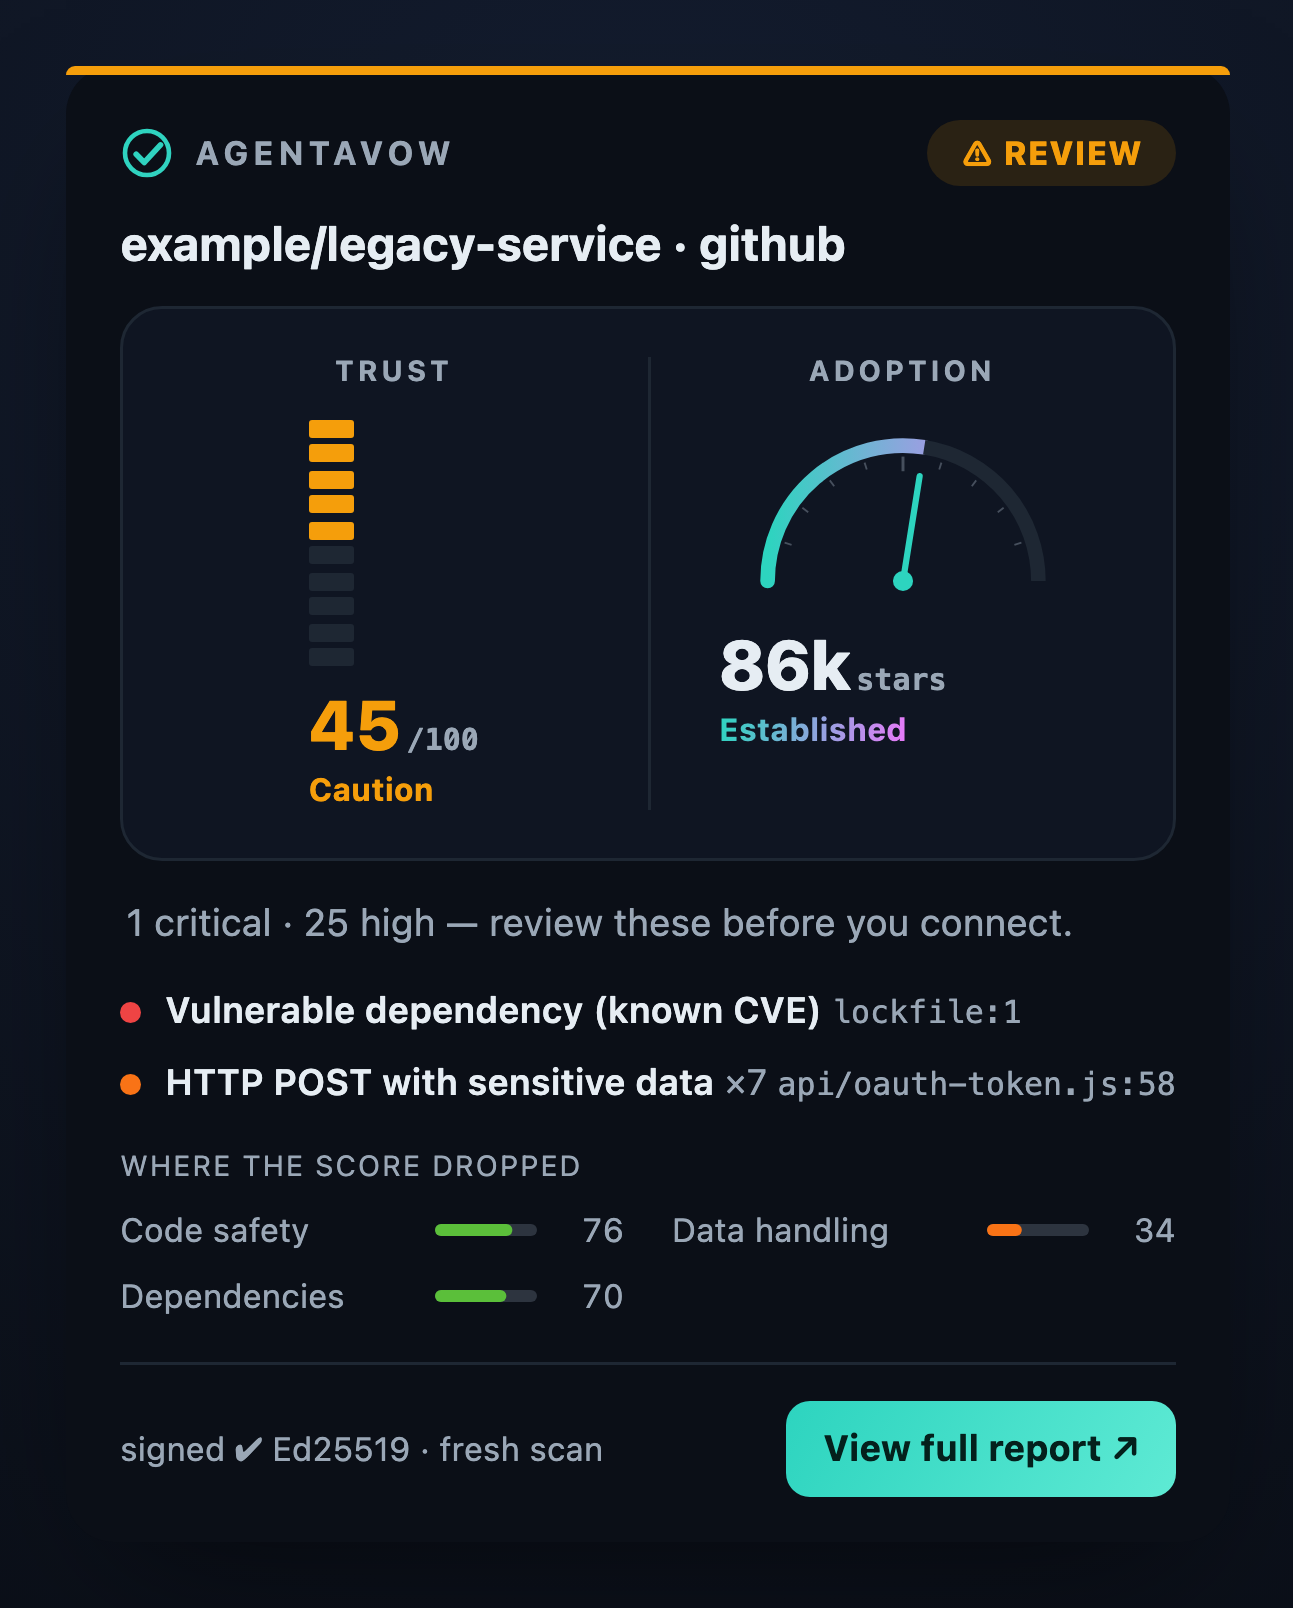
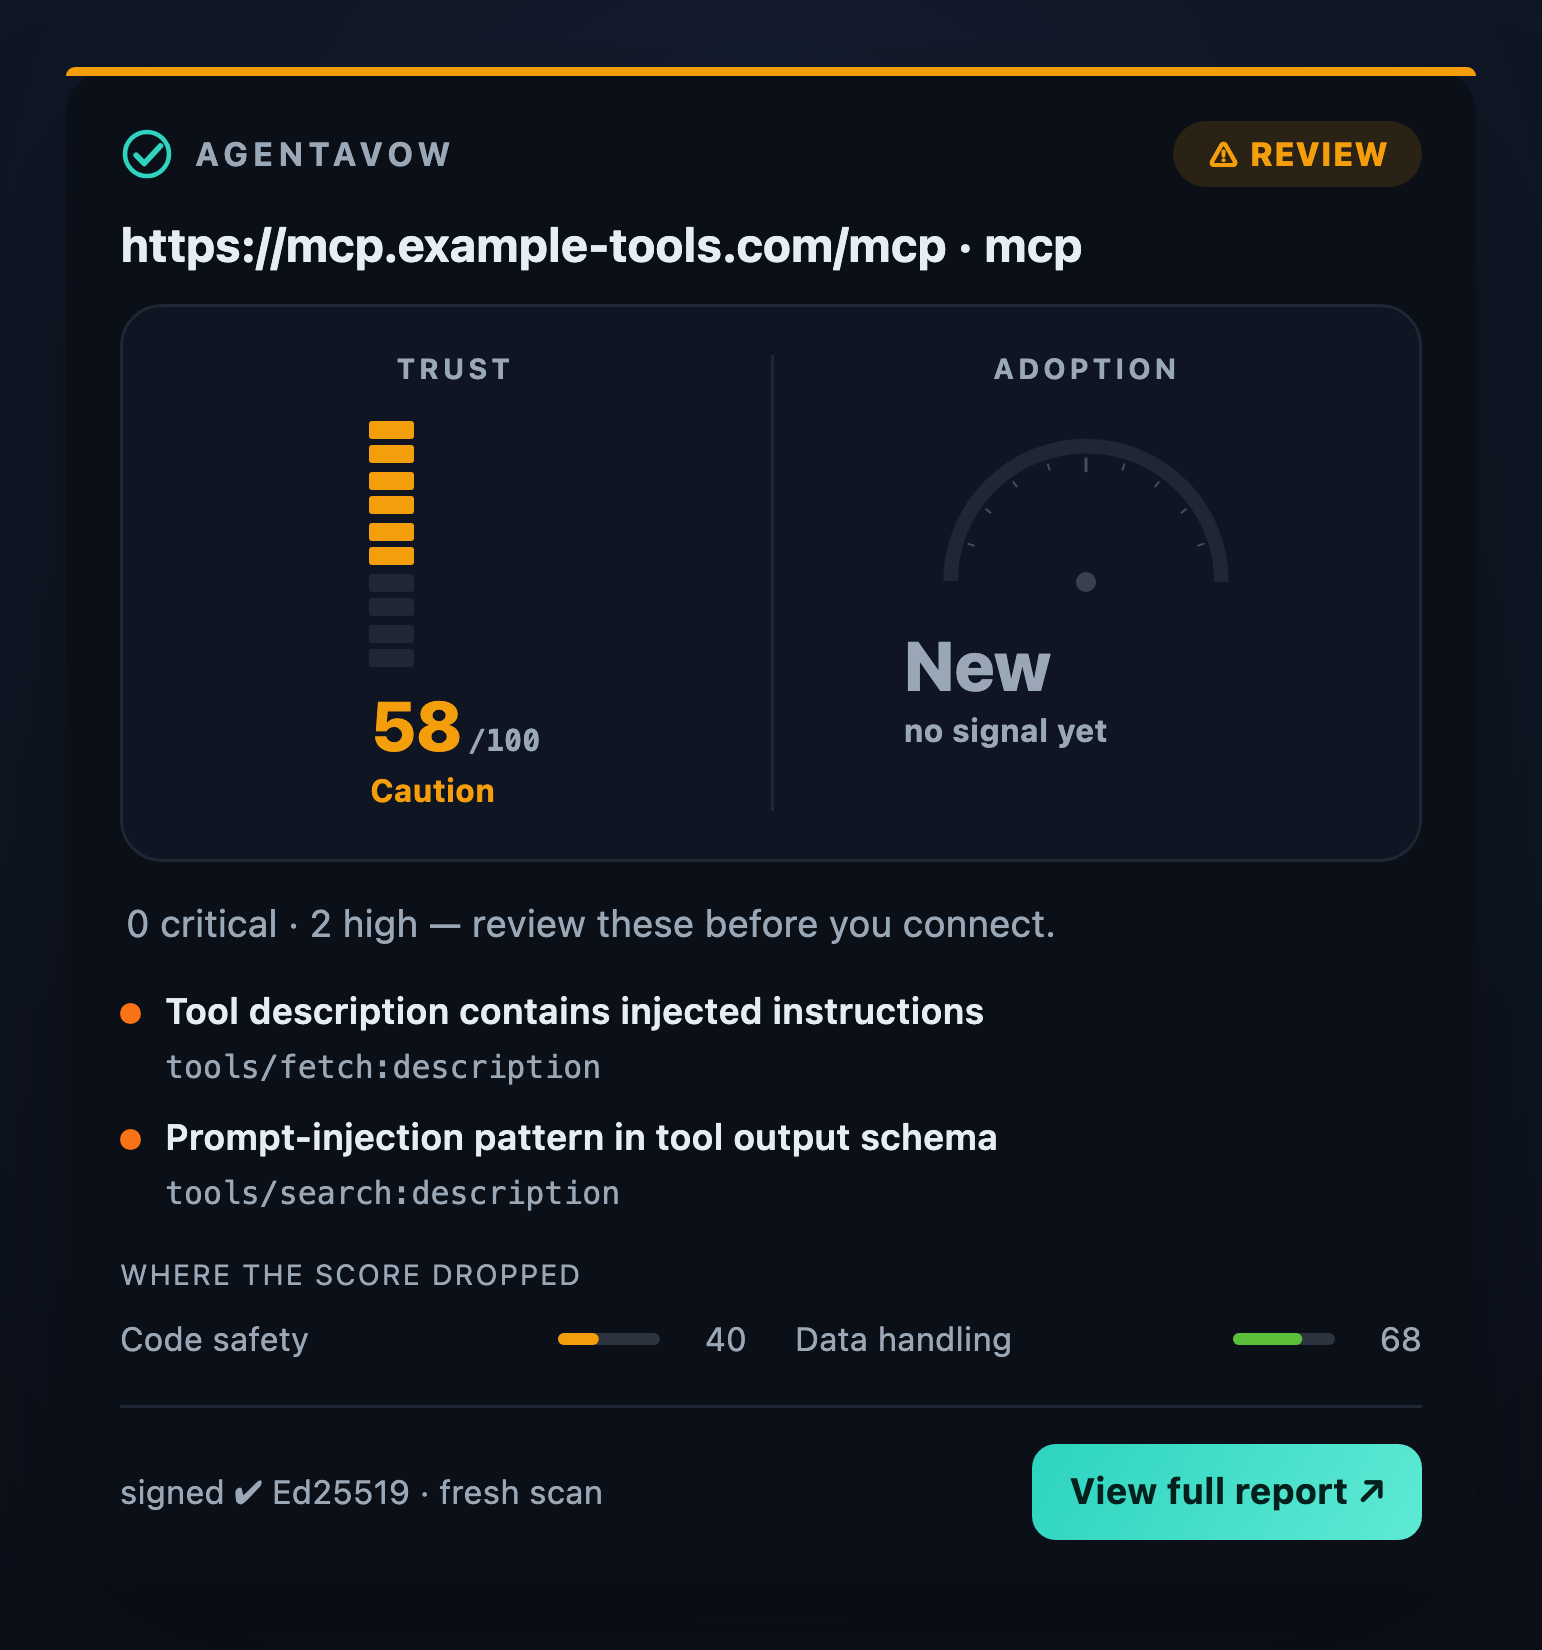
Trust verification and security scanning for AI agents. Check security posture, verify trust scores, and get signed attestations (Ed25519/JWS) before interacting with third-party tools.
AgentAvow Trust MCP Server 配置
使用下面的配置,将此服务器添加到你的 MCP 客户端。
{
  "mcpServers": {
    "agentavow": {
      "type": "http",
      "url": "https://agentavow.com/mcp"
    }
  }
}
AgentAvow Trust MCP Server 工具
工具列表暂未提供
当前收录暂时没有可展示的工具列表,不代表服务没有工具。请查阅项目文档了解支持的能力。
点击上方按钮,直接连接服务器端点实时获取工具列表。
概览
What is AgentAvow Trust?
AgentAvow Trust is an MCP server that grades the safety of anything an AI agent connects to — a GitHub repo, an MCP server, or an npm/PyPI/crates/Docker/Hugging Face package. It returns a signed, 0–100 trust score with a plain safe / needs-review verdict, backed by scan evidence anyone can recompute offline. Read-only and authless: no account, no keys.
How to use AgentAvow Trust
Add the remote server to your MCP client (Claude Code, Cursor, or your own runtime) — no install:
claude mcp add --transport http agentavow https://agentavow.com/mcp
Then ask it to check a tool before you connect: "scan the repo modelcontextprotocol/servers" or "scan the npm package chalk." Every result links to a full report and a signed attestation you can verify offline.
Key features
- Signed, offline-recomputable verdicts — Ed25519/JWS over an RFC 8785 canonical verdict; recompute it byte-for-byte against the public JWKS, no callback required.
- 12-category static analysis — secret hygiene, unsafe code execution, data handling, dependencies, prompt-injection surfaces, and more; every finding points at the exact file and line.
- Scans across surfaces — GitHub repos, live MCP servers (it checks the tool definitions for poisoning/injection), and npm/PyPI/crates/Docker/Hugging Face packages.
- Eight read-only tools — scan_repo, scan_package, scan_mcp_server, verify_trust, check_interaction_safety, lookup_identity, get_trust_badge, about_agentavow.
- Authless — anonymous and read-only; nothing to configure.
Use cases
- Scan an MCP server or package before your agent connects, so an unsafe tool is stopped in the loop rather than found after the fact.
- Gate CI on a minimum score with the GitHub Action or CLI.
- Check the interaction-safety threshold before delegating to or trading with another agent.
- Add a signed trust badge to your README that anyone can verify.
FAQ
- Do I need an account? No — anonymous and read-only.
- Is it free? Yes, checking is free.
- Can I verify a score without trusting AgentAvow? Yes — recompute the canonical verdict and check the Ed25519 signature offline against the public JWKS.
AI 与智能体 分类下的更多 MCP 服务器

Hostinger
hostingerModel Context Protocol (MCP) server for Hostinger API. If you don't want to install or run anything locally, connect directly to Hostinger's hosted MCP server: This opens a browser window to authorize via OAuth. Once app

scvd.store
seancrecordscvd.store is an evidence observatory for agentic commerce. Independent signed observation of what other people's endpoints, artifacts and payments actually did among other things. USDC on Base, Arbitrum One, World Chain
Melaya
Melaya Labs**Melaya gives an AI assistant hands.** It is a remote MCP server, so there is nothing to install and no API key to configure — one URL works in Claude, ChatGPT, Le Chat, Cursor and any MCP client. ### Your Android phon
Lumify Sports Intelligence
LumifyAgent-ready sports intelligence API: live scores, odds, line movement, public betting splits, and explainable bet confidence — via 16 MCP tools at https://lumify.ai/mcp. Get a free key instantly — no signup, email, or ca
Kourier
Kourier AI Inc.Discover flat-rate DeepSeek plans, model limits, API-key instructions, and coding-client setup
评论